Discover how RegCheck® delivers smarter mortgage compliance reviews through loan-specific testing, configurable compliance logic, built-in expertise, and support for evolving industry standards.
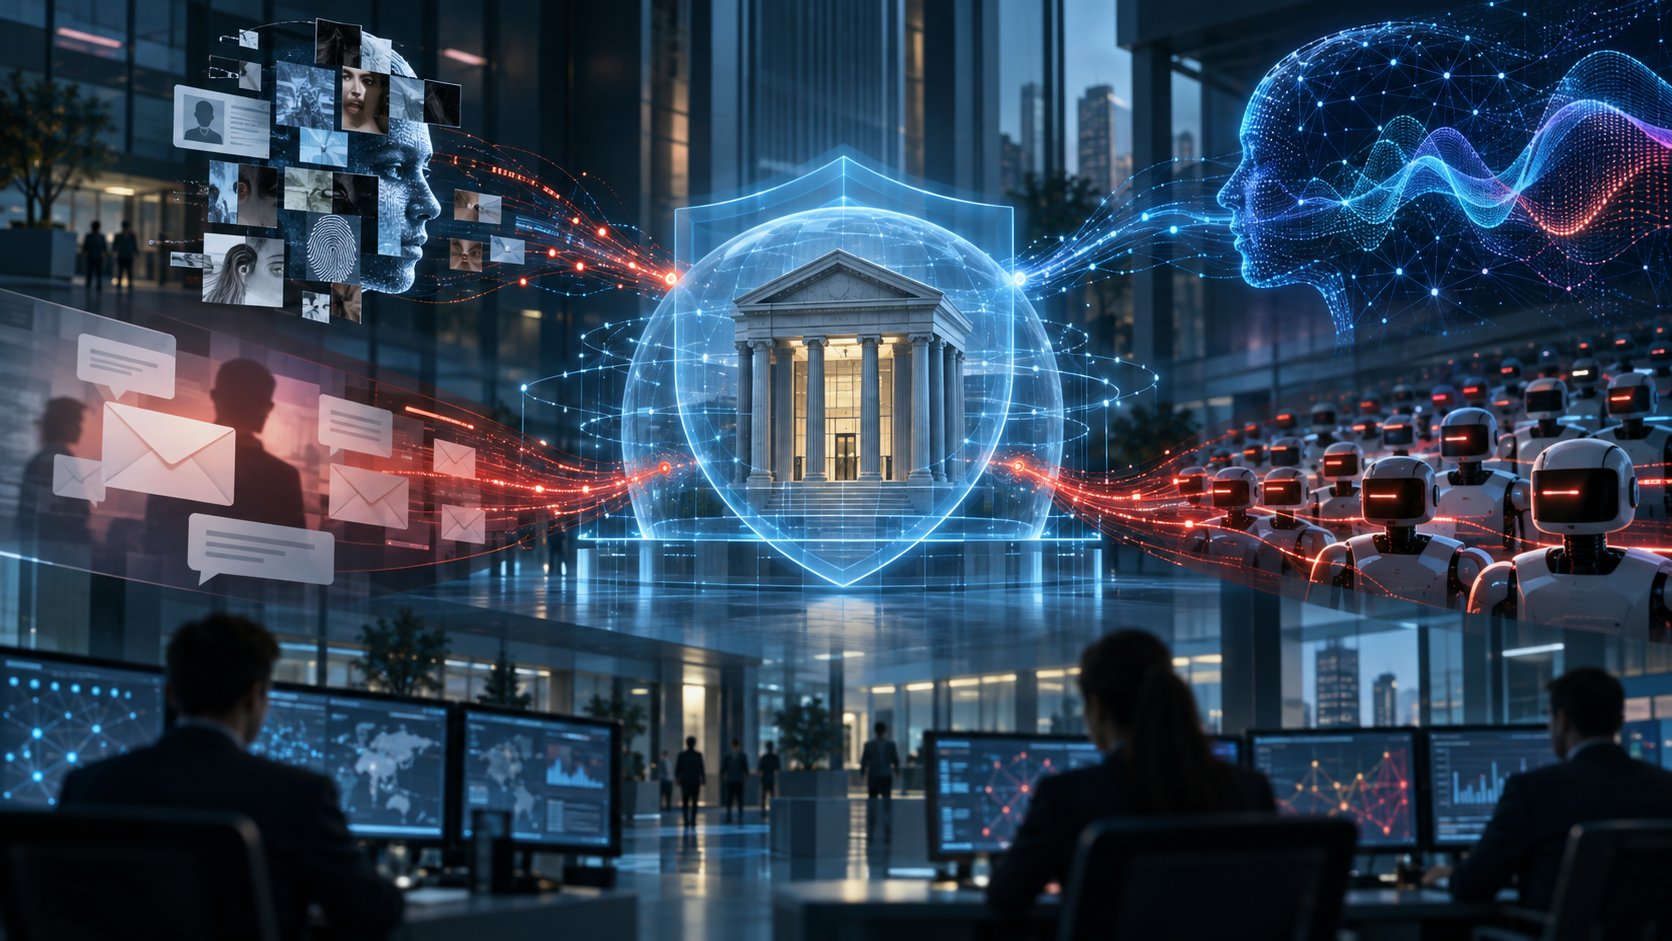
Fraud is becoming more sophisticated and increasingly difficult to distinguish from legitimate customer activity. Criminals are combining stolen information, synthetic identities, social engineering, artificial intelligence (AI), and automation to bypass traditional fraud controls and make fraudulent activity appear increasingly authentic.
A recent FinAi News analysis identified four threats financial institutions should pay particular attention to: new-account fraud, account takeover, customer-authorized scams, and first-party fraud.
While each presents different challenges, they share an important characteristic: detecting them increasingly requires financial institutions to look beyond individual transactions and consider the broader context of customer behavior.
Synthetic identities allow criminals to combine legitimate information with fabricated details to create seemingly legitimate customers. AI can make fraudulent applications and supporting documents increasingly convincing.
Financial institutions should look beyond basic identity verification and consider signals such as device intelligence, application velocity, behavioral indicators, and relationships among accounts.
The question shouldn't simply be, “Can we verify this person?” but rather, “Does this identity make sense in context?”
Account takeover remains a significant threat, but successful authentication doesn't necessarily mean the person behind the session is legitimate. Criminals can obtain passwords and multifactor authentication (MFA) codes through phishing, social engineering, and other techniques.
Security teams should monitor for combinations of events such as a new device, password reset, changed contact information, new beneficiary, and unusual transfer activity.
Individually, these events may be legitimate. Together, they can indicate a compromised account.
Scams present a particularly difficult challenge because the customer may be using their own device and credentials to authorize the transaction.
The FTC reported that consumers lost $15.9 billion to fraud in 2025, underscoring the scale of the problem. Financial institutions therefore need to look beyond the transaction itself and consider behavioral and contextual indicators.
For example, a sudden high-value transfer to a new beneficiary immediately following account changes may warrant greater scrutiny than the same transaction performed as part of a customer's established behavior.
First-party fraud involves legitimate customers intentionally misrepresenting information or abusing financial products. Because the identity itself may be genuine, this type of fraud can be difficult to detect through traditional cybersecurity controls.
Cross-product analytics can help reveal patterns that may not be visible when deposits, credit, payments, and other services are analyzed independently.
AI is making all four threats more scalable. But the answer isn't necessarily another security tool. It may be better integration and analysis of the information financial institutions already have.
Fraud, cybersecurity, identity, AML, and payments teams each see different pieces of the same activity. Bringing those signals together can provide a more complete picture of risk and help institutions identify patterns that might otherwise go unnoticed.
The key shift is from asking:
“Is this transaction fraudulent?”
to asking:
“Does this behavior make sense for this customer, account, and situation?”
In today's fraud environment, the transaction is only one piece of the story. The pattern is the security signal.
As fraud techniques continue to evolve, financial institutions may need to reassess how they connect cybersecurity, identity, fraud, and behavioral signals across their organizations.
Have questions about strengthening your organization's cybersecurity and risk-management approach? Connect with the Asurity Advisors team to learn how we can help.
Discover how RegCheck® delivers smarter mortgage compliance reviews through loan-specific testing, configurable compliance logic, built-in expertise, and support for evolving industry standards.
Discover how Propel™ streamlines DSCR loan production. Generate compliant DSCR documentation nationwide, close faster, and scale investor lending with seamless integration and compliance-first automation.
Find out why a top-ten mortgage lender with a proprietary loan origination system (LOS) needed to convert from a legacy document platform.